The digital sovereignty challenge facing European government agencies has reached a critical point. As regulatory frameworks tighten and geopolitical tensions around data access grow, the choice of communication platform—and crucially, how that platform is deployed—is no longer just an IT decision. It is a matter of legal compliance and data control.
Cloud-hosted Slack, despite its popularity, presents a real compliance challenge for European public sector organizations. The issue isn't the software itself, but what happens when data is held and controlled by a US company operating under American legal jurisdiction. This creates conflicts with European data protection requirements that are difficult to resolve contractually.
One important clarification upfront: the CLOUD Act problem applies specifically to cloud-hosted deployments where a US vendor controls the data. An on-premises deployment of any software—regardless of where the vendor is based—places data under the control of the organization running it, not the vendor. Vendor nationality matters primarily when that vendor hosts your data.
This guide is for IT decision-makers, compliance officers, and procurement specialists who need to understand their options and choose a platform that guarantees full data control.
01What makes a communication platform "sovereign"?
Deployment model is the defining factor
The most important—and often misunderstood—principle of digital sovereignty is that it is about data control, not vendor nationality. A European agency self-hosting any communication platform on its own infrastructure controls that data entirely. The vendor, wherever it is based, has no access to the data and cannot be compelled to hand it over under any foreign law.
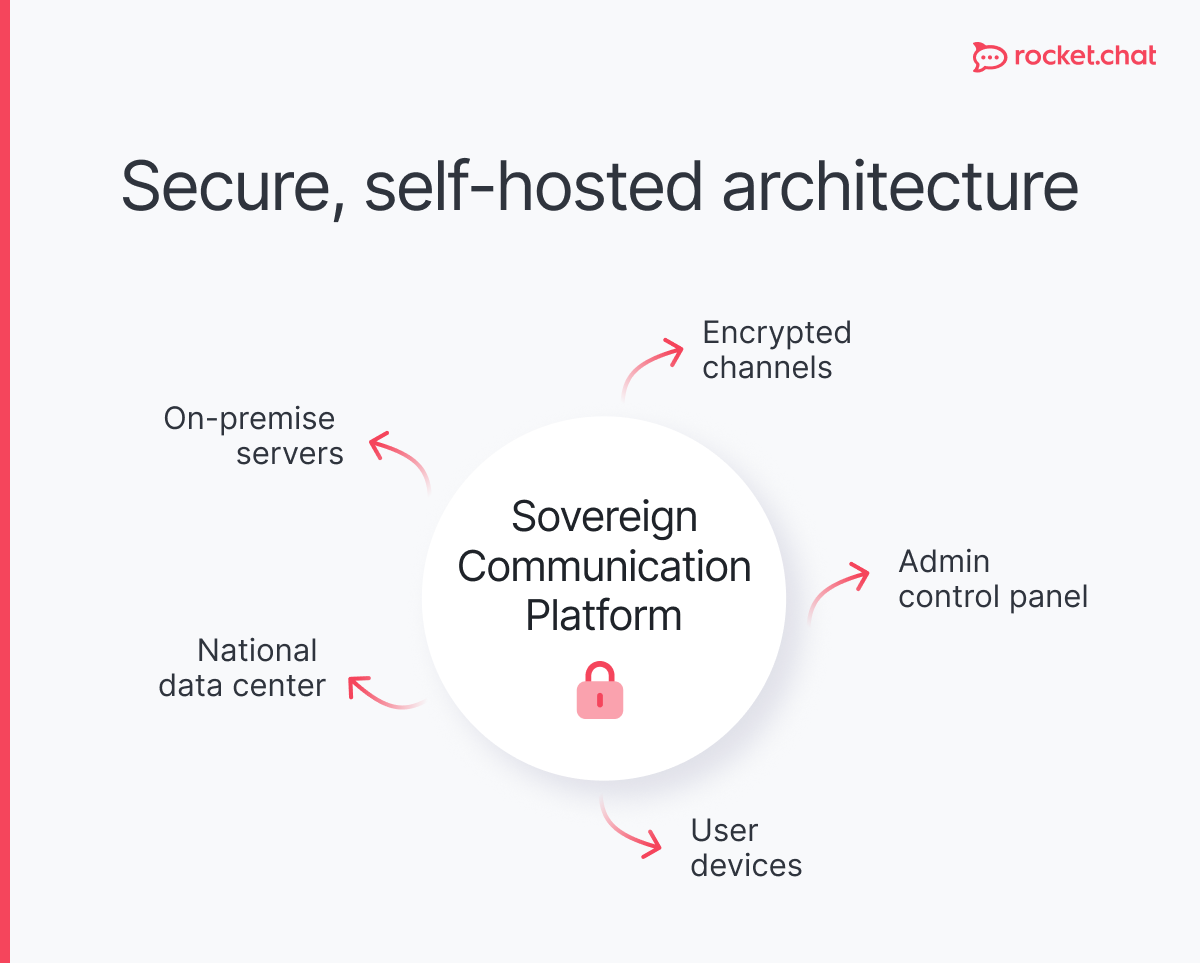
The question to ask is not "where is this company headquartered?" but "who controls our data, and under what legal framework?" Two deployment scenarios ensure sovereignty: self-hosting on agency-controlled infrastructure, or using a cloud provider operating exclusively under EU jurisdiction.
Cloud-hosted services from vendors subject to foreign jurisdiction—regardless of server location—can only offer a sub-ideal level of guarantee, because the vendor retains data control.
Key characteristics to look for
A sovereign deployment should meet these criteria. Full data ownership means your organization, not a vendor, decides who accesses your communications. On-premises or EU-cloud deployment options give you the choice to host on your own infrastructure or with a provider exclusively under EU law.
Open-source code enables your security team to audit for vulnerabilities independently, rather than relying on vendor claims.
End-to-end encryption with agency-controlled keys ensures that even infrastructure providers cannot read your data. And audit logging and data retention controls must be configurable to your compliance requirements, not the vendor's defaults.
02Leading sovereign Slack alternatives for European government
Rocket.Chat
Rocket.Chat is an open-source secure communications platform with AI capabilities that can run entirely on-premises or in EU cloud environments. A company with a global presence, Rocket.Chat is built for organizations that require complete deployment flexibility and full data sovereignty.
Sovereignty profile: Rocket.Chat can be fully self-hosted on agency infrastructure or deployed via EU cloud providers. The open-source MIT license means complete code transparency for security audits. Because the agency controls the deployment, no external party—including Rocket.Chat—has access to the data. This eliminates CLOUD Act exposure regardless of the vendor's country of origin.
Key features:
- Secure team messaging with organized channels, threads, and direct messages
- End-to-end encryption for sensitive communications, including support for encrypted messaging apps standards
- Bring-your-own AI/LLM capabilities — agencies can run AI assistance entirely on-premises, maintaining data sovereignty even at the AI layer
- Air-gapped deployment for classified networks and high-security environments
- Extensive integration ecosystem with over 1,000 apps and services
- Advanced compliance features including audit logs and configurable data retention
- Federation for inter-agency collaboration (Matrix protocol)
Best suited for: Government agencies requiring AI-enhanced secure collaboration while maintaining full data sovereignty, organizations operating across multiple security classification levels, and agencies that want maximum deployment flexibility including air-gapped environments.
Pricing: Self-hosted free/open-source option for core functionality; Enterprise licenses for advanced features and dedicated government support.
Mattermost
Mattermost is an open-source collaboration platform with a security-first design, widely adopted by technical and operational teams that need robust controls and familiar workflows.
Sovereignty profile: Mattermost's primary model is self-hosted deployment, giving agencies full control over data location. Its open-source core under MIT/Apache licenses provides code transparency, and no telemetry or external data transmission occurs by default. EU-compatible hosting is fully supported.
Key features:
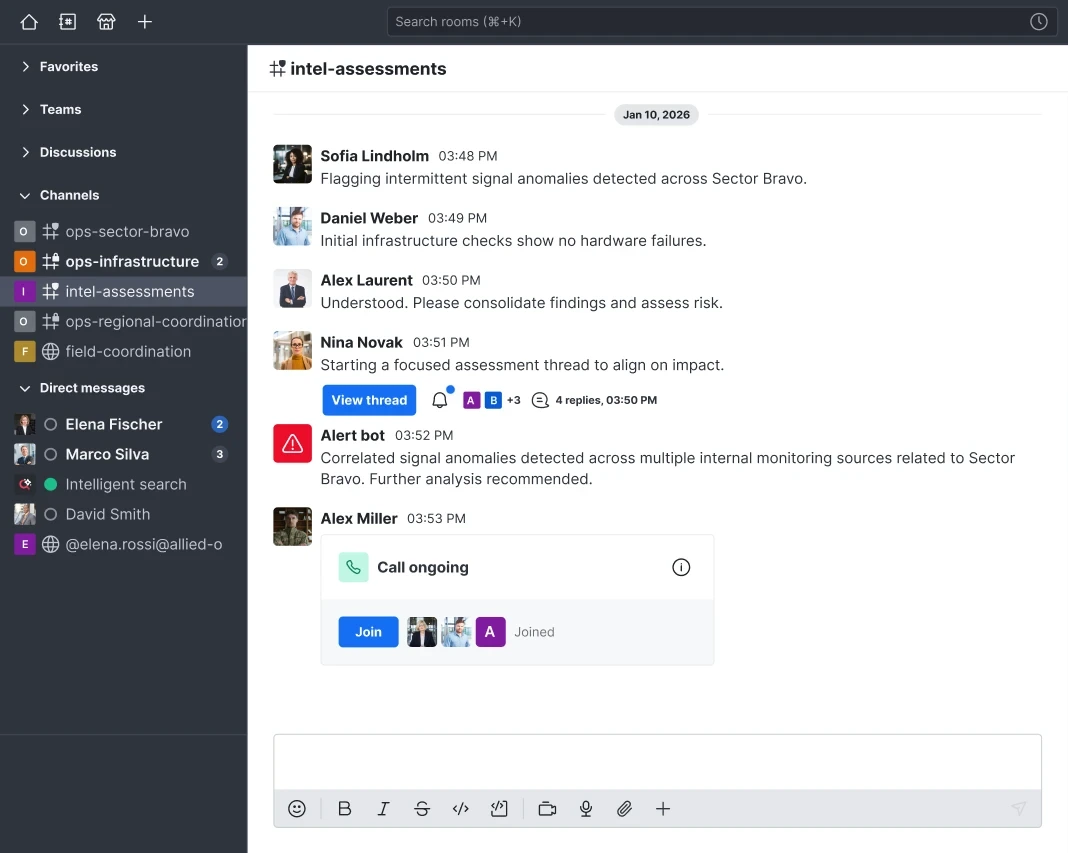
- Slack-like interface that significantly reduces transition friction for users
- Strong DevOps and technical team integrations for IT and development workflows
- Playbooks for automated incident response and repeatable processes
- Voice calling and screen sharing for workplace team communication
- Compliance and e-discovery tools built into the platform
Best suited for: Technical teams, DevOps organizations, and agencies where Slack familiarity matters and developer workflow integration is a priority.
Pricing: Free self-hosted edition with full core features; Professional and Enterprise tiers for advanced capabilities and support.
Element (Matrix protocol)
Element is a decentralized communication platform built on the open Matrix protocol, offering a fundamentally different architecture based on federation rather than centralized control.
Sovereignty profile: Element's decentralized design means there is no single point of control or failure. Agencies self-host their own homeserver, maintaining complete data ownership. Element is a UK/Germany-based company operating under EU jurisdiction. The Matrix protocol is an open standard, and deployments can federate with other Matrix servers or run in full isolation. Element holds government certifications in France and Germany.
Key features:
- End-to-end encryption by default across all communications
- Federated architecture enables secure government chat between different agencies without sharing infrastructure
- Bridges to other platforms including Slack and Microsoft Teams for transition flexibility
- Cross-platform support across web, mobile, and desktop
- Government-grade security certifications from multiple EU member states, including for military messaging and military chat use cases
Best suited for: Agencies requiring inter-governmental collaboration across organizations, maximum resilience through decentralization, and those operating in environments where federation between agencies is a priority.
Pricing: Free self-hosted option using the Matrix protocol; Element Enterprise for managed hosting and premium support.
Quick comparison
| Criteria | Rocket.Chat | Mattermost | Element |
|---|---|---|---|
| Deployment model | Self-hosted or EU cloud | Self-hosted primary | Self-hosted or federated |
| Open source | MIT License | MIT/Apache | Apache License |
| E2E encryption | Available | Available | By default |
| Air-gap capable | Yes | Yes | Yes |
| On-premises AI/LLM | Yes | No | No |
| Slack-like UX | Similar | Very similar | Different |
| Integration ecosystem | Extensive (1,000+) | Strong (DevOps) | Moderate (bridges) |
| Best for | AI-enhanced collaboration, flexibility | Technical teams, DevOps | Inter-agency federation |
03Why cloud-hosted Slack creates compliance challenges
The US CLOUD Act
The Clarifying Lawful Overseas Use of Data Act (CLOUD Act), enacted in 2018, allows US authorities to compel US-based companies to provide data they control, regardless of where servers are located. The critical word is "control." When Slack hosts your data—even in EU data centers—it retains control and remains subject to CLOUD Act requests.
According to research from the European Parliament, this extraterritorial reach overrides contractual data residency commitments. US authorities can also issue warrants with gag orders that legally prohibit Slack from notifying you that your data has been accessed, making contractual transparency clauses effectively unenforceable.
If your agency self-hosts any platform on its own infrastructure, this risk disappears entirely — the vendor no longer controls the data and cannot be compelled to produce it.
GDPR and Schrems II
The General Data Protection Regulation requires that data transfers outside the EU meet strict adequacy standards. The landmark Schrems II decision of July 2020 invalidated the EU-US Privacy Shield, with the Court of Justice of the European Union finding that US surveillance programs do not provide adequate protection for EU citizens' data. Even with the subsequent EU-US Data Privacy Framework adopted in 2023, legal uncertainty persists for encrypted messaging services controlled by US vendors.
NIS2 Directive
The NIS2 Directive, which EU Member States were required to transpose by October 17, 2024, establishes cybersecurity requirements across 18 critical sectors. According to the European Commission, NIS2 introduces stricter supply chain security requirements and mandates 24-hour incident reporting for significant events.
For agencies classified as essential or important entities, using cloud-hosted platforms where a foreign vendor controls data access makes it difficult to meet supply chain security obligations or guarantee full incident visibility. Self-hosted deployments resolve this by returning control to the agency. For further reading on how these requirements intersect with organizational security, the compliance implications are significant.
04How to evaluate and choose between platforms
Start with your deployment model
Before comparing features, decide on your deployment approach:
- Self-hosting on agency infrastructure gives maximum control and eliminates vendor jurisdiction concerns entirely—but requires dedicated IT resources.
- EU cloud hosting from providers operating exclusively under EU law is a strong alternative for agencies without infrastructure capacity.
- A hybrid approach, using cloud for general communications and self-hosted for classified work, suits agencies with mixed security requirements.
For cloud deployments, verify that the provider has no foreign parent company that could be subject to the CLOUD Act or equivalent laws. Request written contractual guarantees about who has administrative access and under what legal framework.
Key selection criteria
Compliance and certifications should be your first filter. Does the platform hold ISO 27001 certification? Has it achieved government security clearances in EU member states? These provide independent validation beyond vendor claims.
Security features to prioritize include end-to-end encryption with agency-controlled keys, granular access controls, tamper-evident audit logs, and configurable data retention policies aligned to your legal requirements. For government messaging use cases, these are non-negotiable baseline requirements. Reviewing frameworks like the NIST Cybersecurity Framework can help structure your internal security assessment.
Functionality should match your operational needs: channels, direct messaging, file sharing, search, mobile access, and external collaboration capabilities.
Evaluate integration support for LDAP, SAML, SSO, and your existing tools. If your agency is also evaluating other tools beyond Slack, our guide on Microsoft Teams alternatives for European government covers similar grounds. When comparing options, also consider which platforms rank among the most secure messaging apps for enterprise and government use.
Total cost of ownership must account for licensing, infrastructure, implementation, training, and ongoing maintenance. Open-source platforms offer free core editions, but factor in staff time and support contracts for an accurate five-year comparison.
Vendor stability matters for long-term deployments. Assess the size of the user community, quality of documentation, and availability of professional government support options.
Pilot before committing
Run a structured pilot with 20-50 representative users across roles and technical abilities for 4-8 weeks. Define clear success criteria upfront—feature coverage, user satisfaction, system performance—and use results to build your internal business case before full procurement.
05Planning your migration
Migrating from cloud-hosted Slack to a sovereign platform typically takes 3-6 months for most government agencies, depending on size and complexity. The process breaks into four phases.
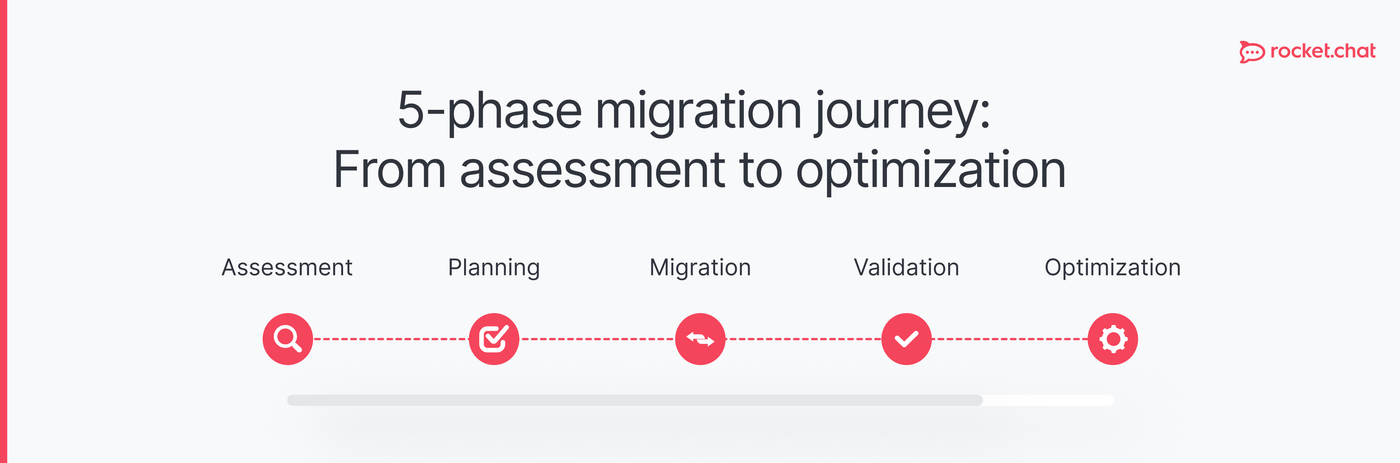
Planning (weeks 1-4): Finalize platform selection, assemble a cross-functional team including IT, security, and change management, and map integration dependencies early. Delaying integration work is one of the most common and costly mistakes in migrations.
Infrastructure and setup (weeks 4-8): Deploy the platform, configure security and compliance settings, establish data residency parameters, and test integrations before any users migrate.
Data migration and user transition (weeks 8-16): Export Slack data, migrate by department in phases, and run platforms in parallel during the handover period. Provide dedicated user support and training during this window—underestimating training needs is the other most common failure point.
Validation (weeks 16-20): Verify data completeness, confirm compliance requirements are met, address user feedback, and decommission Slack once adoption is stable.
For agencies considering air-gapped collaboration environments or military-grade security requirements, additional validation phases for security certification may extend this timeline.
06Conclusion
The compliance case for European government agencies to move away from cloud-hosted Slack is clear. When a US vendor controls your data, CLOUD Act exposure, GDPR conflicts, and NIS2 supply chain requirements create risks that cannot be fully resolved contractually. The solution is straightforward: choose a platform that can be deployed on infrastructure you control.
Rocket.Chat, Mattermost, and Element each offer credible paths to full data sovereignty, with self-hosted and EU-cloud options that eliminate foreign jurisdiction concerns. Of these, Rocket.Chat stands out for agencies that also want sovereign AI capabilities—the ability to run on-premises LLMs without data ever leaving agency-controlled infrastructure.
The transition requires investment, but the outcome is communications infrastructure your agency fully owns and controls, aligned with European regulations and future-proofed against an increasingly complex legal landscape. Start your evaluation now, run a structured pilot, and build a migration plan that puts your agency in control of its own data.
Frequently asked questions
Why can't we just use Slack's EU hosting option?
Slack's EU data residency doesn't resolve the core issue: Slack still controls your data. The CLOUD Act follows data control, not server geography. If your agency self-hosted any communication platform on its own infrastructure, vendor nationality becomes irrelevant—the vendor no longer controls the data and cannot be compelled to produce it.
What is the US CLOUD Act and how does it affect Slack?
The CLOUD Act allows US authorities to compel American companies to provide data they control, anywhere in the world. For cloud-hosted Slack, this means EU government communications could be accessed without your knowledge. Crucially, this risk is tied to data control, not simply to Slack being American. A self-hosted deployment eliminates this exposure entirely.
Are sovereign communication platforms as feature-rich as Slack?
Modern sovereign platforms match or exceed Slack's core functionality. They offer organized channels, direct messaging, file sharing, integrations, and mobile apps. Some provide capabilities Slack lacks, like on-premises AI and air-gapped deployment. The feature gap has largely closed, with sovereignty the key differentiator.
How much does it cost to switch from Slack to a sovereign platform?
Costs vary by deployment model and scale. Open-source self-hosted platforms carry no licensing cost but require infrastructure and staff time. Managed EU cloud services typically run €3-15 per user monthly. Factor in migration, training, and potential consulting fees. Most agencies find total costs comparable to Slack while gaining full data control.
Can sovereign platforms integrate with our existing tools?
Yes. Leading platforms support LDAP, SAML, and OAuth for authentication and offer APIs for custom government system integrations. Evaluate integration support for your specific tools—identity providers, ticketing systems, and document management—as a primary selection criterion.
What does "open source" mean and why does it matter for sovereignty?
Open source means the platform's source code is publicly available for inspection. Your security team can audit for vulnerabilities or backdoors rather than trusting vendor claims. It also prevents vendor lock-in—you are never dependent on a single company's roadmap or pricing decisions.
Will our employees resist switching from Slack?
Resistance is normal but manageable. Choose platforms with familiar interfaces to reduce learning curves. Communicate the compliance and security rationale clearly. Run pilots with influential early adopters who can champion the platform internally, and provide structured training during rollout.
How long does it take to migrate from Slack to a sovereign alternative?
Most government agencies complete migration in 3-6 months. Small agencies may finish in 2-3 months; large multi-site organizations may need up to 9 months. Key variables are infrastructure readiness, data volume, integration complexity, and the phased rollout approach.
Do we need to host the platform ourselves or can we use EU cloud hosting?
Both maintain sovereignty if implemented correctly. Self-hosting provides maximum control but demands IT resources. EU cloud providers operating exclusively under EU law offer a managed alternative. Some agencies use EU cloud for general communications and self-host for classified environments.
Which European government agencies have already migrated?
Several EU member states have moved to sovereign platforms. Austria's Federal Ministry for Economy, Energy and Tourism migrated 1,200 employees to European open-source alternatives. France and Germany have certified specific platforms for government use. Many agencies do not publicize platform choices for security reasons, but the trend toward sovereign deployments is accelerating across Europe.